Quick version
I looked at two Minecraft products from InPvP, the company behind Mineville. Dawn Client let a Minecraft server reach an outdated, unsandboxed browser. BedrockBuddy let uploaded content reach a vulnerable native image decoder. Both findings earned me a $500 bounty, and I kicked it off with a single prompt in P4ndora's new P4ndora Offensive Lab.
Some people collect Minecraft skins. I seem to collect InPvP bug bounties. Sorry, PizzaMC! But you are a legend for paying bounties.
Round one: Dawn Client
Dawn, formerly Feather Client, had a pretty interesting idea of what a Minecraft server should be allowed to do.
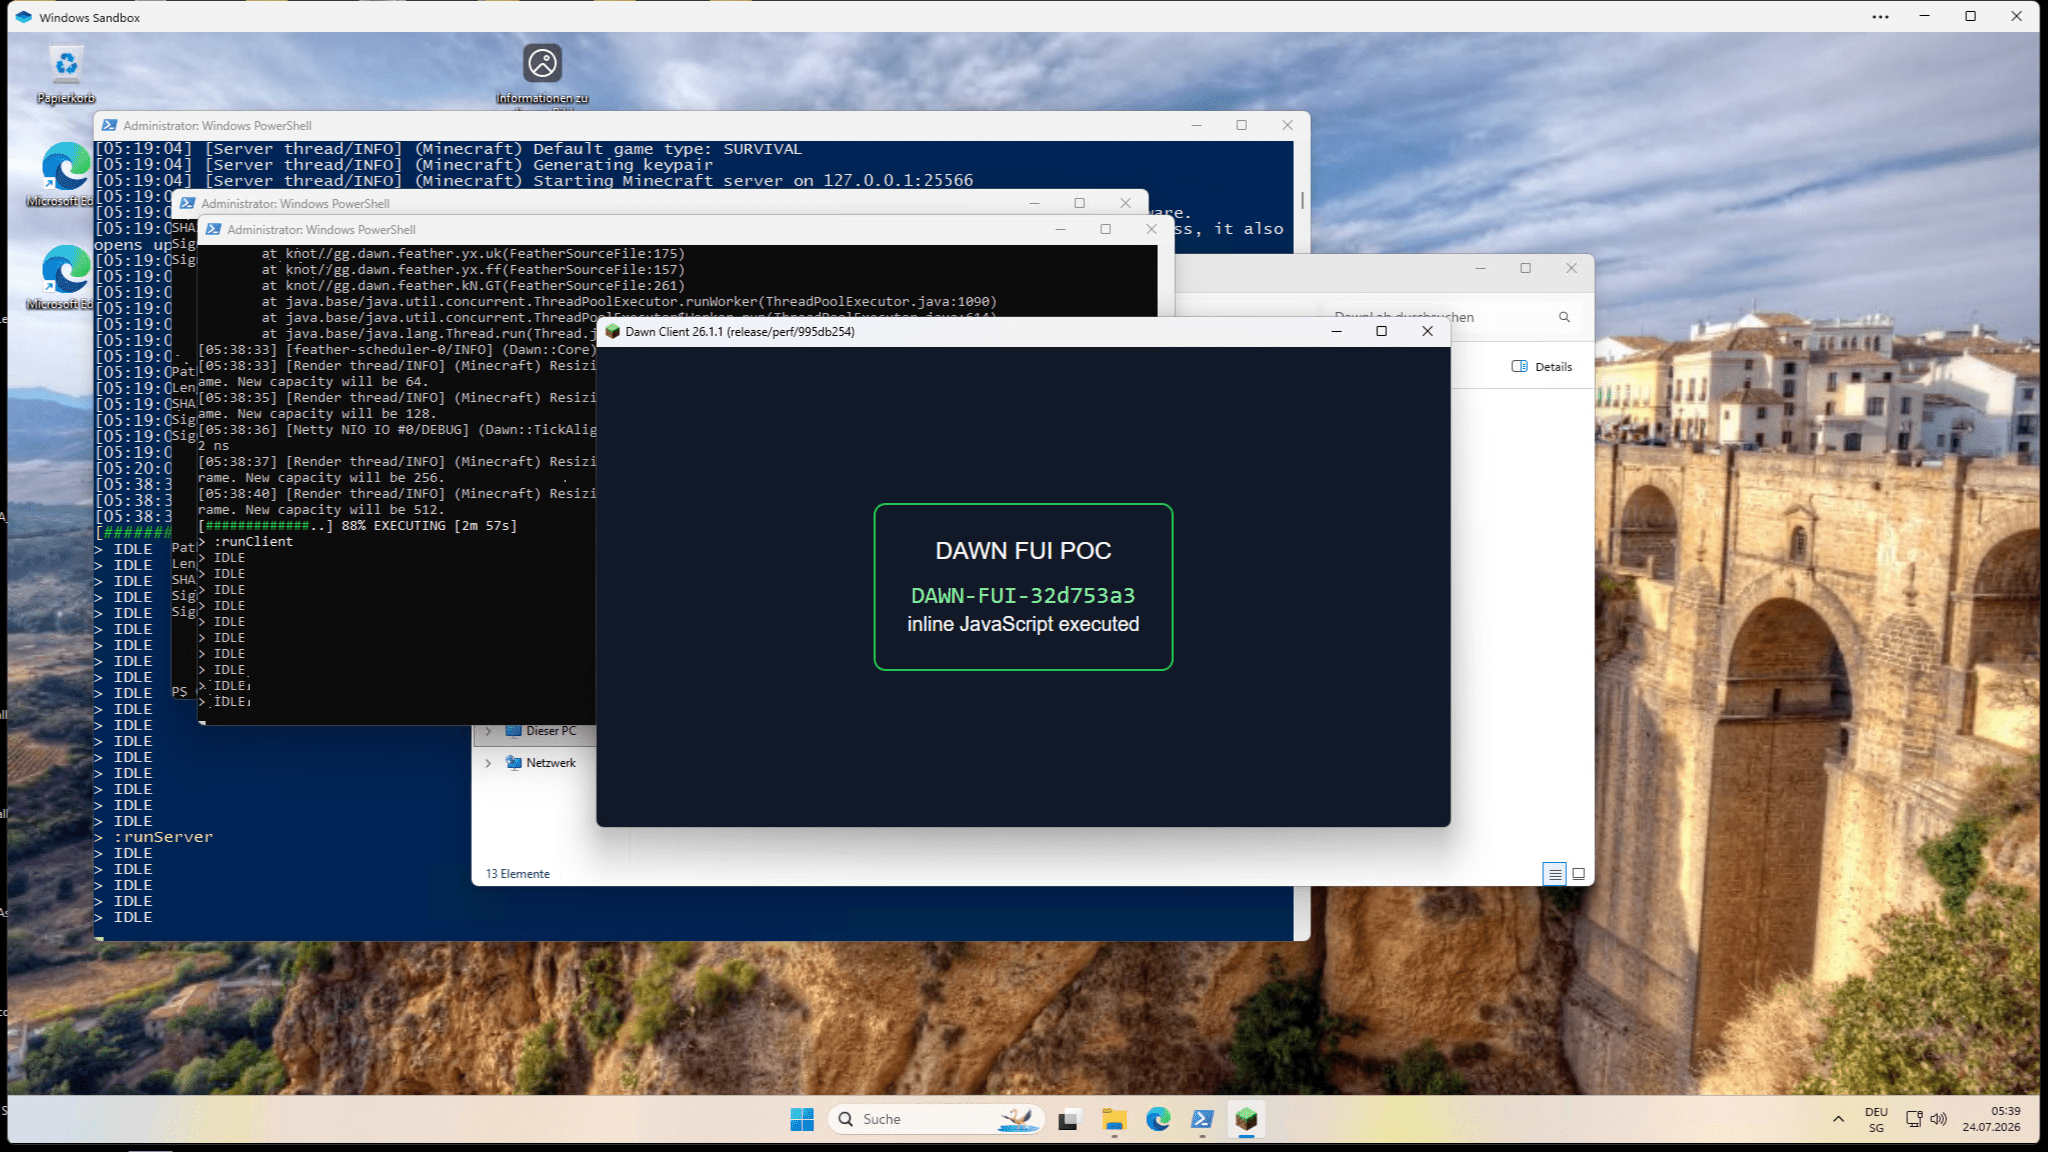
Join a server, receive a custom game packet, and the client could load HTML chosen by that server inside its embedded browser. JavaScript ran immediately. No second click, no approval, no magical "are you sure?" popup.
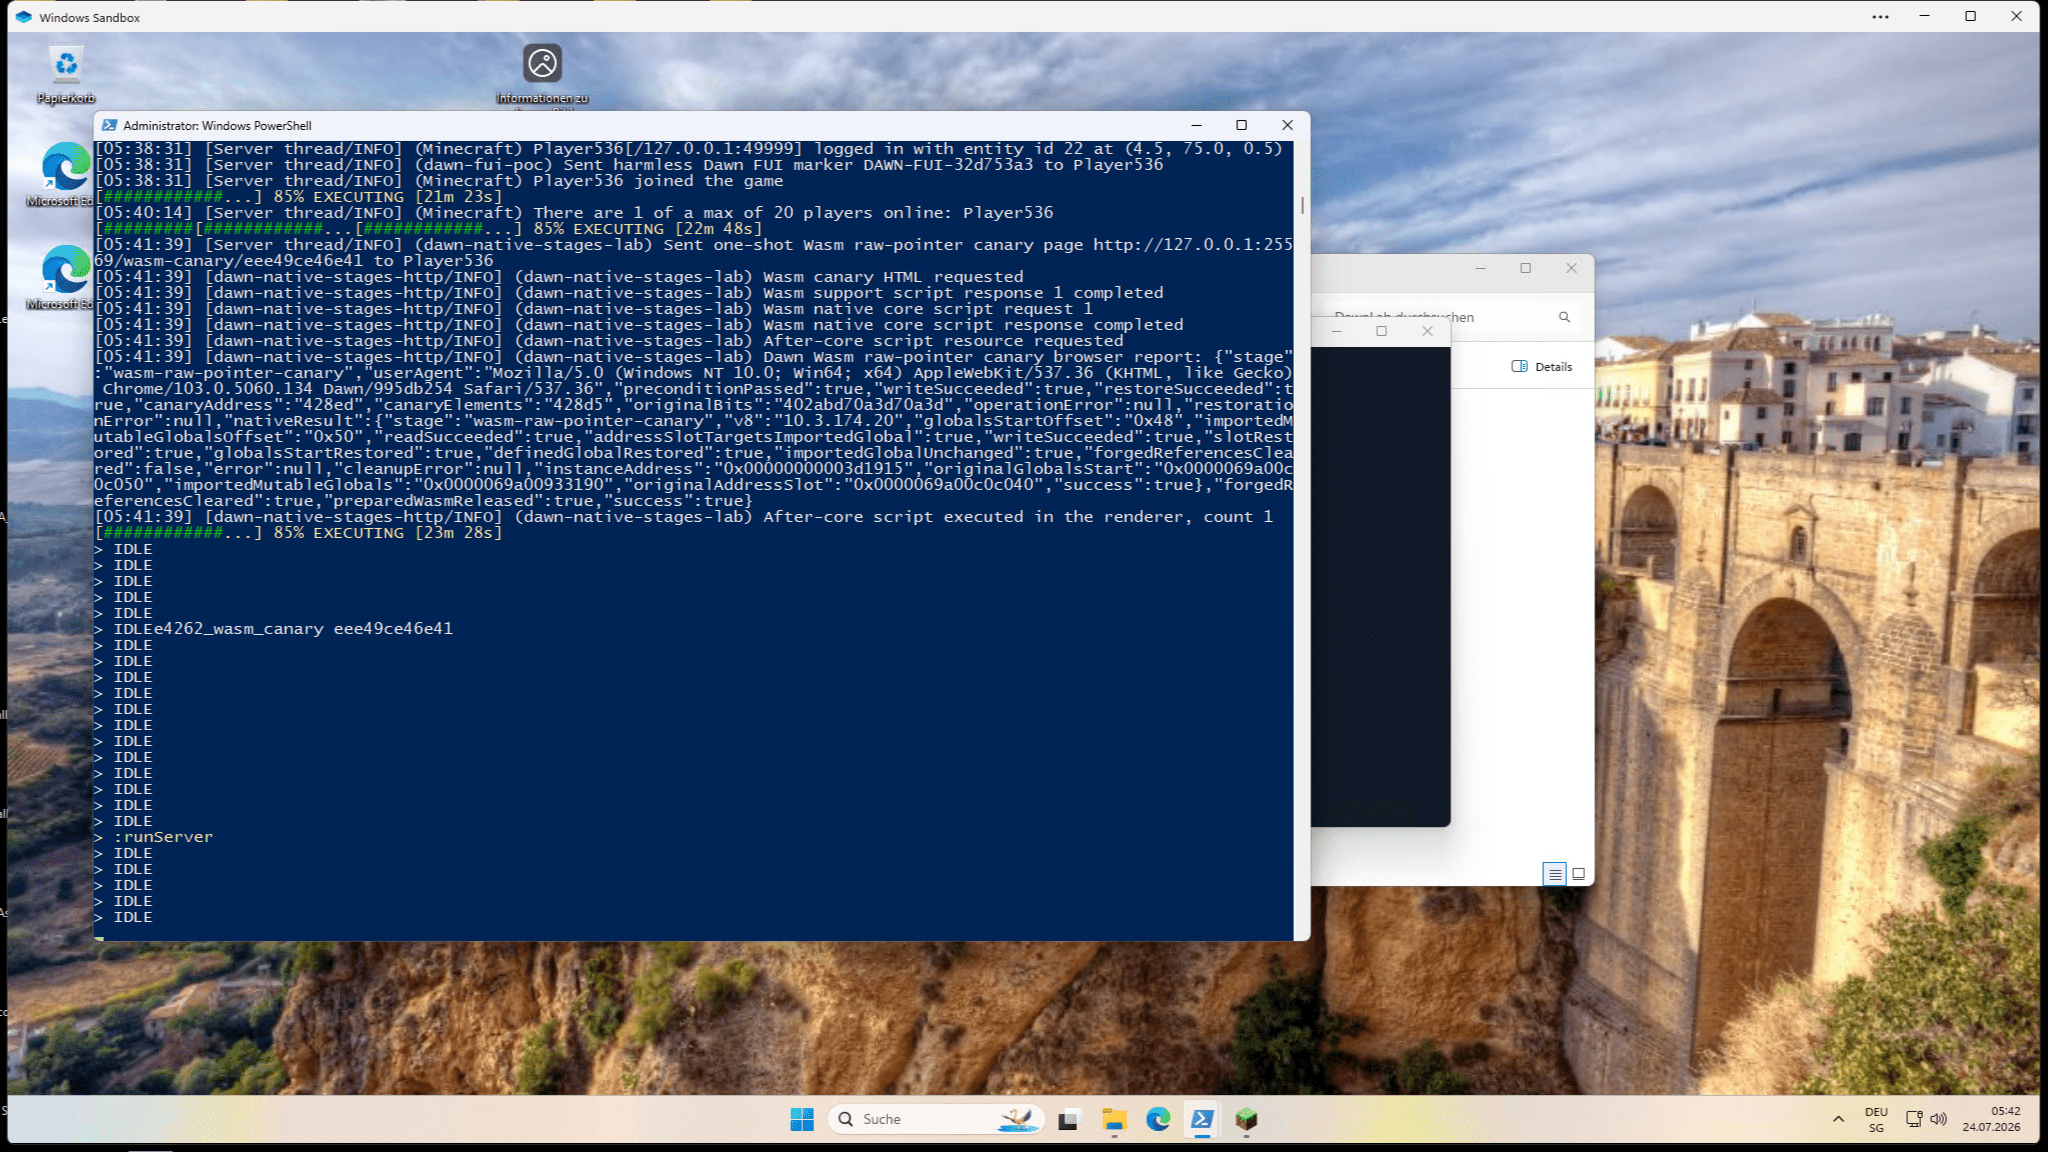
That would already be a nasty phishing surface. The fun part was what happened underneath. The tested Windows build shipped Chromium 103 with its CEF sandbox disabled. In a disposable VM, I used that delivery path to trigger CVE-2022-4262 and verify controlled native memory reads and writes in the actual
Not a finished OS-level RCE, but a very real route toward one. Minecraft really did not need a browser exploit side quest.
Round two: BedrockBuddy
A while later, InPvP launched BedrockBuddy. A fresh website, a fresh attack surface. Naturally, I couldn't resist.
This time, the problem was hiding in something as ordinary as uploading an image.
BedrockBuddy lets users upload images, which are then processed by Next.js. Normally, the website should verify that an uploaded file is actually an image before making it publicly accessible.
Well, that verification had a little problem. You could upload a file and access it before the validation was completed.
Here's where it gets interesting.
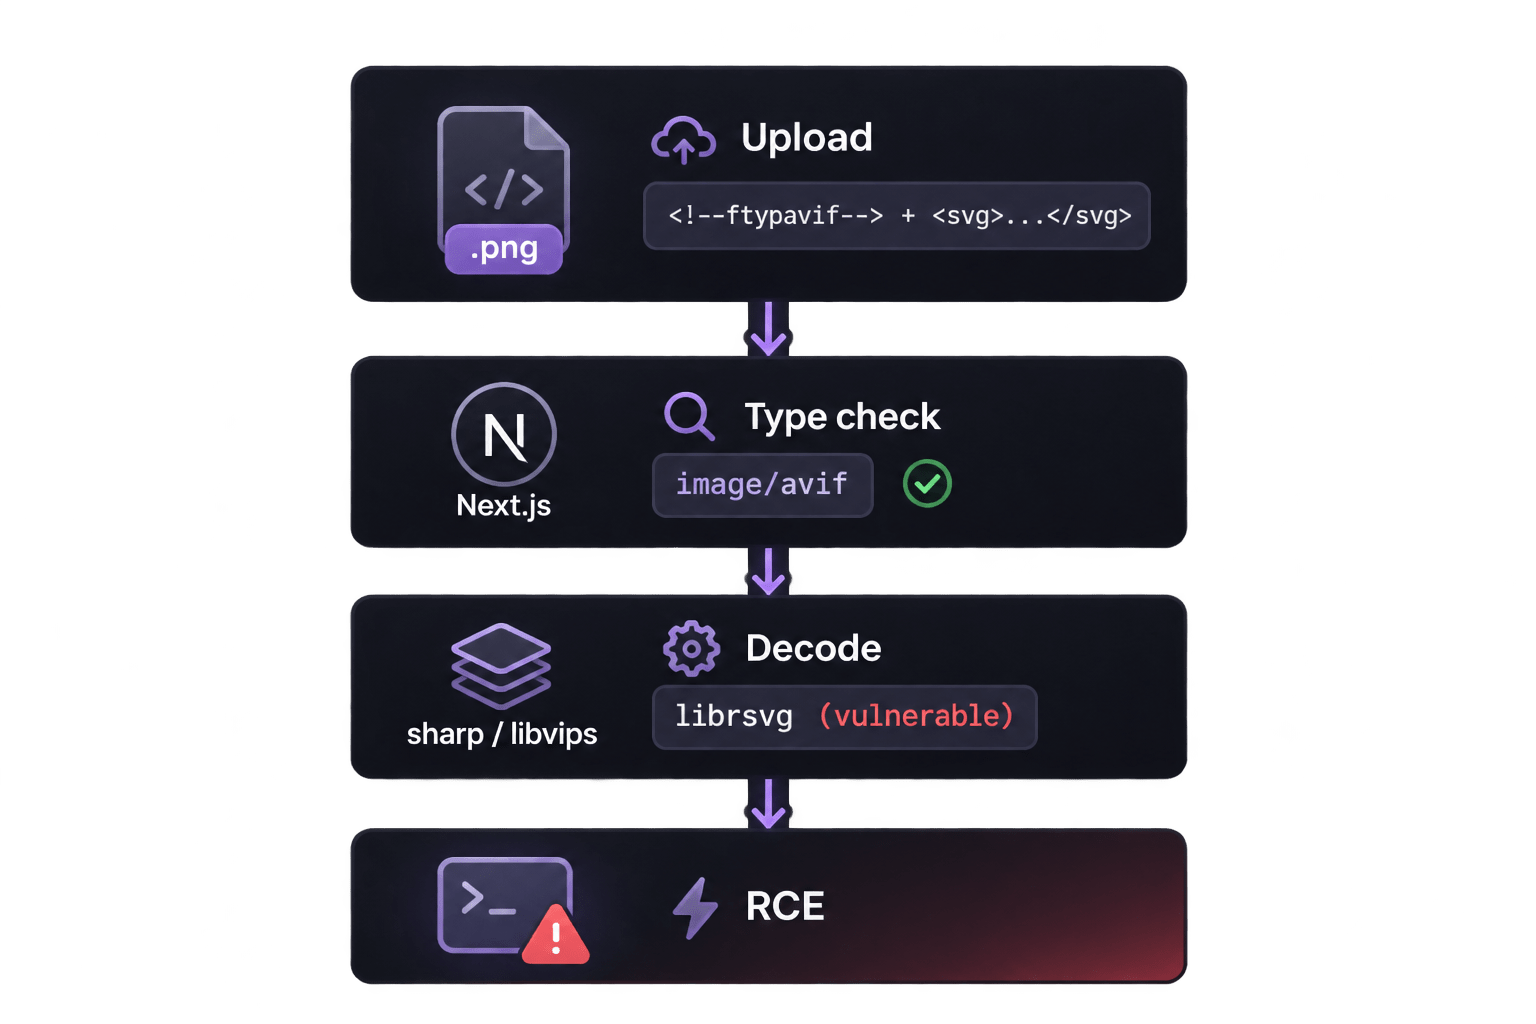
I uploaded a tiny 110-byte file that looked like a PNG upload but actually contained SVG (XML) content. A specially crafted comment at the beginning tricked Next.js into treating it as an allowed AVIF image.
The image optimizer then passed the file to Sharp and libvips, which recognized the actual SVG content and handed it to librsvg 2.62.91, a version affected by CVE-2026-96889, a use-after-free vulnerability.
In other words, I could make the server feed attacker-controlled content into a vulnerable native image decoder.
And the best part? The live server happily converted my fake image into real WebP and JPEG files, confirming that the entire parsing chain was reachable.
To safely verify the vulnerability, I recreated the decoder stack locally.
Same payload, different result. Exactly what you want to see when validating a vulnerability.
I deliberately avoided crashing the production server or attempting full code execution. The live tests confirmed the vulnerable parsing path, while the local tests demonstrated memory corruption.
The result? A $500 bug bounty.
The one-prompt part
Here's the bit I'm especially excited about. I started the BedrockBuddy investigation with one prompt in Pandora Offensive Lab, the offensive security product we're building.
It isn't a chatbot throwing random CVE names at you. It runs inside an isolated cloud machine with real security tools, a browser, web search and a defined target scope. You give it the task, it investigates and collects evidence. I still review the results and reproduce risky findings safely, but it takes a lot of the repetitive work off my hands.
Two prompts, two real findings, and two $500 payouts. I wouldn't call it an infinite money glitch, but it's a pretty good field test.
If you do pentesting or bug bounties and want to try it, check out Pandora Offensive Lab. Access is reviewed because, well, giving an AI a hacking workstation probably deserves a little gatekeeping.
I looked at two Minecraft products from InPvP, the company behind Mineville. Dawn Client let a Minecraft server reach an outdated, unsandboxed browser. BedrockBuddy let uploaded content reach a vulnerable native image decoder. Both findings earned me a $500 bounty, and I kicked it off with a single prompt in P4ndora's new P4ndora Offensive Lab.
Some people collect Minecraft skins. I seem to collect InPvP bug bounties. Sorry, PizzaMC! But you are a legend for paying bounties.
Round one: Dawn Client
Dawn, formerly Feather Client, had a pretty interesting idea of what a Minecraft server should be allowed to do.
Join a server, receive a custom game packet, and the client could load HTML chosen by that server inside its embedded browser. JavaScript ran immediately. No second click, no approval, no magical "are you sure?" popup.
That would already be a nasty phishing surface. The fun part was what happened underneath. The tested Windows build shipped Chromium 103 with its CEF sandbox disabled. In a disposable VM, I used that delivery path to trigger CVE-2022-4262 and verify controlled native memory reads and writes in the actual
FeatherWebHelper.exe process.Not a finished OS-level RCE, but a very real route toward one. Minecraft really did not need a browser exploit side quest.
Round two: BedrockBuddy
A while later, InPvP launched BedrockBuddy. A fresh website, a fresh attack surface. Naturally, I couldn't resist.
This time, the problem was hiding in something as ordinary as uploading an image.
BedrockBuddy lets users upload images, which are then processed by Next.js. Normally, the website should verify that an uploaded file is actually an image before making it publicly accessible.
Well, that verification had a little problem. You could upload a file and access it before the validation was completed.
Here's where it gets interesting.
I uploaded a tiny 110-byte file that looked like a PNG upload but actually contained SVG (XML) content. A specially crafted comment at the beginning tricked Next.js into treating it as an allowed AVIF image.
The image optimizer then passed the file to Sharp and libvips, which recognized the actual SVG content and handed it to librsvg 2.62.91, a version affected by CVE-2026-96889, a use-after-free vulnerability.
In other words, I could make the server feed attacker-controlled content into a vulnerable native image decoder.
And the best part? The live server happily converted my fake image into real WebP and JPEG files, confirming that the entire parsing chain was reachable.
To safely verify the vulnerability, I recreated the decoder stack locally.
Code:
Vulnerable version  -> SIGSEGV (crash)
Patched version     -> Works normally
Same payload, different result. Exactly what you want to see when validating a vulnerability.
I deliberately avoided crashing the production server or attempting full code execution. The live tests confirmed the vulnerable parsing path, while the local tests demonstrated memory corruption.
The result? A $500 bug bounty.
The one-prompt part
Here's the bit I'm especially excited about. I started the BedrockBuddy investigation with one prompt in Pandora Offensive Lab, the offensive security product we're building.
It isn't a chatbot throwing random CVE names at you. It runs inside an isolated cloud machine with real security tools, a browser, web search and a defined target scope. You give it the task, it investigates and collects evidence. I still review the results and reproduce risky findings safely, but it takes a lot of the repetitive work off my hands.
Two prompts, two real findings, and two $500 payouts. I wouldn't call it an infinite money glitch, but it's a pretty good field test.
If you do pentesting or bug bounties and want to try it, check out Pandora Offensive Lab. Access is reviewed because, well, giving an AI a hacking workstation probably deserves a little gatekeeping.
